1. Parties and background
This agreement is between the customer the customer named in the offer as controller (”the Customer”) and ScanSay as processor (”ScanSay”). It forms part of the main agreement (the Terms). In case of conflict on personal data matters, this agreement prevails.
2. Subject matter, nature and purpose
ScanSay processes personal data on the Customer’s behalf in order to:
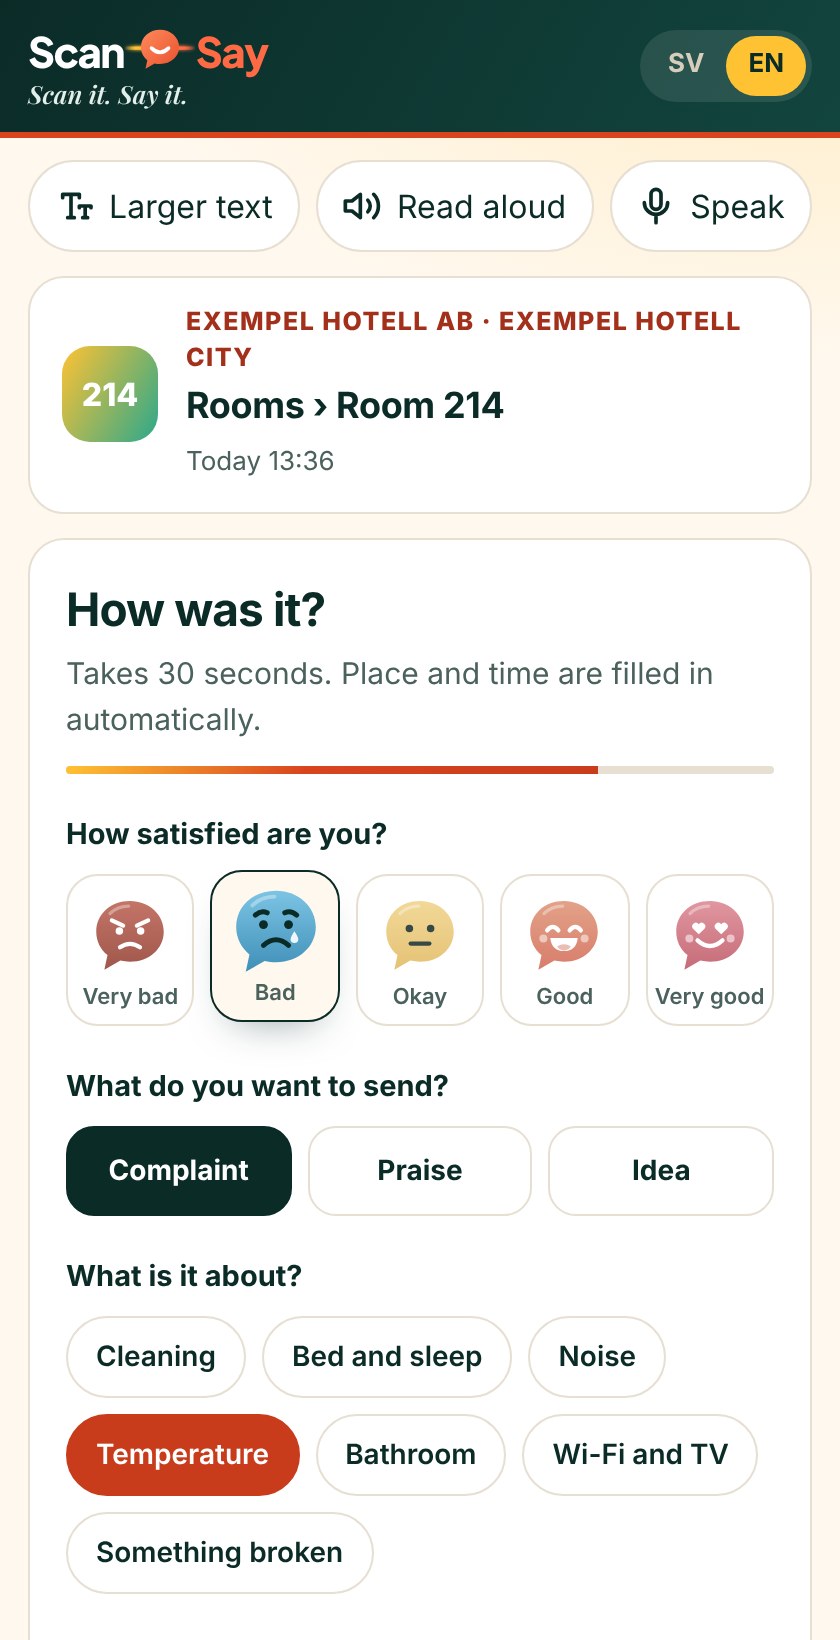
- receive feedback through QR codes at the Customer’s places,
- sort, route and alert on cases to the right users,
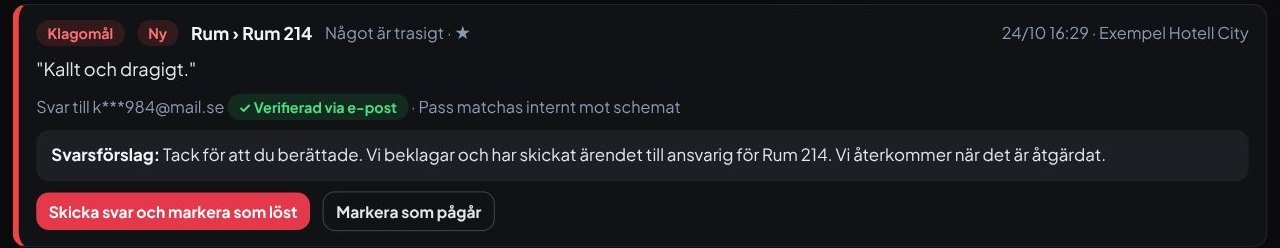
- send confirmation and replies to the person who gave feedback,
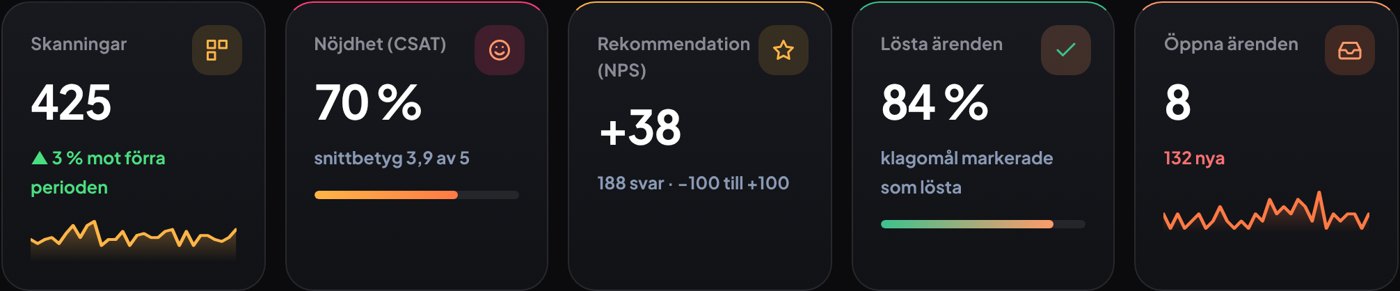
- produce statistics, reports and, if the Customer chose the Insight plan, AI summaries and suggested replies.
3. Data subjects and personal data
Data subjects: people giving feedback, the Customer’s users with accounts, and the Customer’s employees if the Customer has enabled shift linking.
- Feedback: email address, optional name, message, optional photo, rating, topic, place code and time.
- Technical data for spam and abuse protection: truncated IP address and browser type, kept for at most 30 days.
- Users: name, email, role and login log.
- Shifts (only if enabled): vehicle, place and time linked to an internal staff ID.
The service is not intended for special categories of data under Article 9 GDPR, criminal offence data or national ID numbers. The form asks people not to share such data and not to photograph other people. The Customer must not design topics or questions that ask for such data.
4. Duration and retention
Processing lasts as long as the main agreement. Feedback is deleted automatically after the retention period the Customer chooses (6–24 months, default 12). After that only anonymous statistics remain.
5. The Customer’s instructions
ScanSay processes personal data only on the Customer’s documented instructions, meaning this agreement and the settings the Customer makes in the service. ScanSay informs the Customer immediately if it believes an instruction breaks data protection law.
ScanSay does not process the data for its own purposes, never sells it and does not use it to train AI models.
6. Confidentiality
Everyone working for ScanSay with access to the personal data is bound by written confidentiality and may only process it to deliver the service.
7. Security
ScanSay takes technical and organisational measures under Article 32 GDPR. They are described in Annex 2 and reviewed at least once a year.
8. Sub-processors
The Customer gives general prior authorisation for the sub-processors in Annex 3. ScanSay notifies the Customer at least 30 days before adding or replacing one. The Customer may object on reasonable grounds and, if no solution is found, terminate the service at no cost.
ScanSay signs written agreements with sub-processors containing the same obligations as this agreement and remains fully liable to the Customer for their processing.
9. Transfers outside the EU/EEA
All personal data is stored and processed in the EU/EEA, including by sub-processors and in AI features. Transfer to a third country may only happen with the Customer’s written approval and with safeguards under Chapter V GDPR.
10. Data subject rights
ScanSay helps the Customer answer requests for access, rectification, erasure, restriction and objection, including with export and deletion tools in the service. A request received directly by ScanSay is forwarded to the Customer without undue delay.
11. Personal data breaches
ScanSay notifies the Customer without undue delay, and no later than 24 hours after discovering a breach. The notice contains the information needed under Article 33(3) GDPR, so the Customer can report to the Swedish Authority for Privacy Protection (IMY) within 72 hours and inform data subjects where required.
12. Impact assessment
ScanSay assists the Customer with information for a data protection impact assessment and any prior consultation with IMY under Articles 35–36 GDPR.
13. Staff and employment law
Named staff statistics are off by default. The Customer is responsible for union consultation under MBL, informing employees and having a legal basis before enabling the feature. The service makes no automated decisions about employees under Article 22 GDPR, and the AI features never assess individual employees.
14. Public sector
If the Customer is a public authority, municipality or region, feedback may become official documents. The Customer is responsible for the Public Access to Information and Secrecy Act (OSL) and archiving rules. ScanSay helps with export in a readable format.
15. When the agreement ends
The Customer can export its data for 30 days after the agreement ends. ScanSay then deletes all personal data within 30 days, and from backups within 90 days. ScanSay confirms deletion in writing on request.
16. Audits
ScanSay gives the Customer the information needed to show compliance with this agreement. The Customer, or an independent auditor bound by confidentiality, may audit once a year with 30 days’ notice, and additionally after a breach or at IMY’s request.
17. Liability, changes and governing law
Liability follows Article 82 GDPR and the main agreement. Changes must be in writing. Swedish law applies and disputes are settled by Swedish courts, with Gothenburg District Court as first instance.
Annex 1. Processing summary
| Purpose | Feedback, case handling, replies, statistics and AI summaries |
| Data subjects | People giving feedback, users, employees (if enabled) |
| Data | Email, optional name, message, photo, rating, place, time, technical log |
| Retention | 6–24 months as chosen by the Customer, default 12 |
| Location | EU/EEA only |
Annex 2. Technical and organisational measures
- Encryption in transit (TLS 1.2 or higher) and at rest (AES-256).
- Role-based access and least privilege. Staff never see the data subject’s email.
- Two-factor authentication for administrators and for ScanSay’s own access.
- Logging of logins and access to cases, kept for 12 months.
- Daily encrypted backups in the EU, restore tested at least once a year.
- Spam and abuse protection with rate limiting.
- Ongoing security updates and vulnerability scanning.
- Incident handling routine with notification within 24 hours.
- AI features receive only the text needed, without email or name.
Annex 3. Sub-processors
| Sub-processor | Service | Location | Data |
|---|
| Hosting provider in the EU | Hosting and storage | EU EU/EEA | All service data |
| Email service in the EU | Confirmations and replies | EU | Email, case number, reply text |
| SMS service in the EU | Alerts to users | EU | User phone number, alert text |
| AI service in the EU | Summaries and suggested replies (Insight) | EU, no training on data | Message text and statistics, without email or name |
Providers in brackets are filled in before launch. Each provider must have a data processing agreement and process data in the EU/EEA.
Signatures: Customer: name and date · ScanSay: name and date